Managed Detection & Response
Managed detection and response with investigation and response guidance.
Managed Detection & Response
MDR can help organizations improve detection, clarify investigations, and prepare response actions within an agreed service scope.
The Challenge
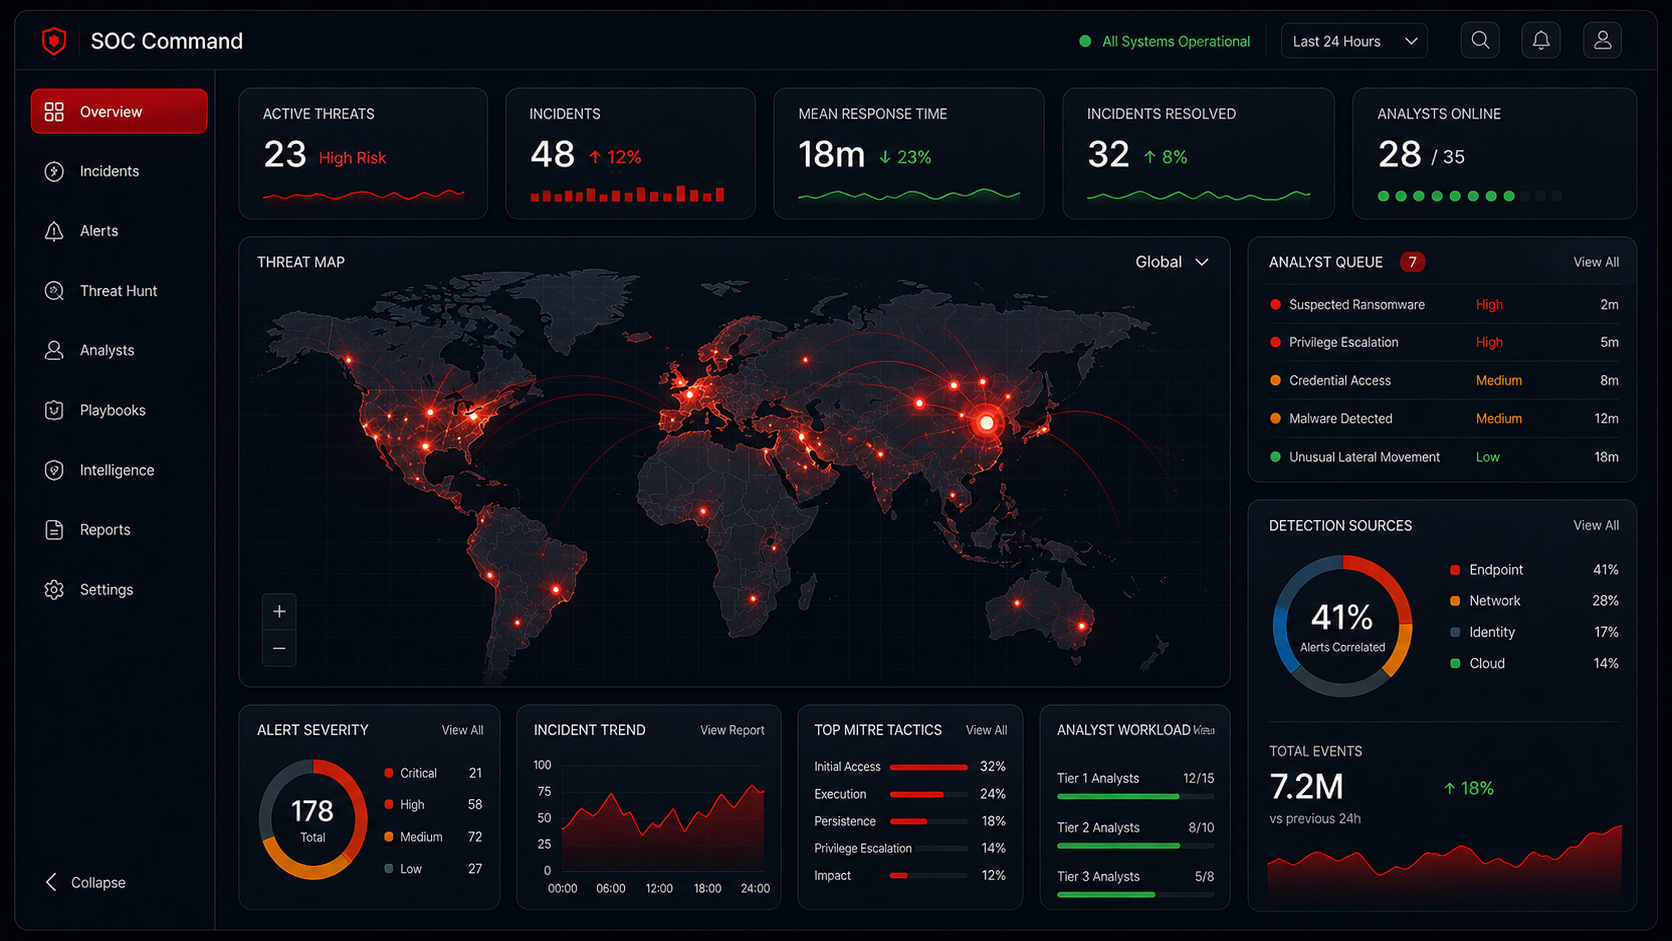
From Alert Overload To Operational Clarity.
Security tools produce thousands of signals. MDR turns that noise into a smaller set of validated incidents your team can trust.
Coverage
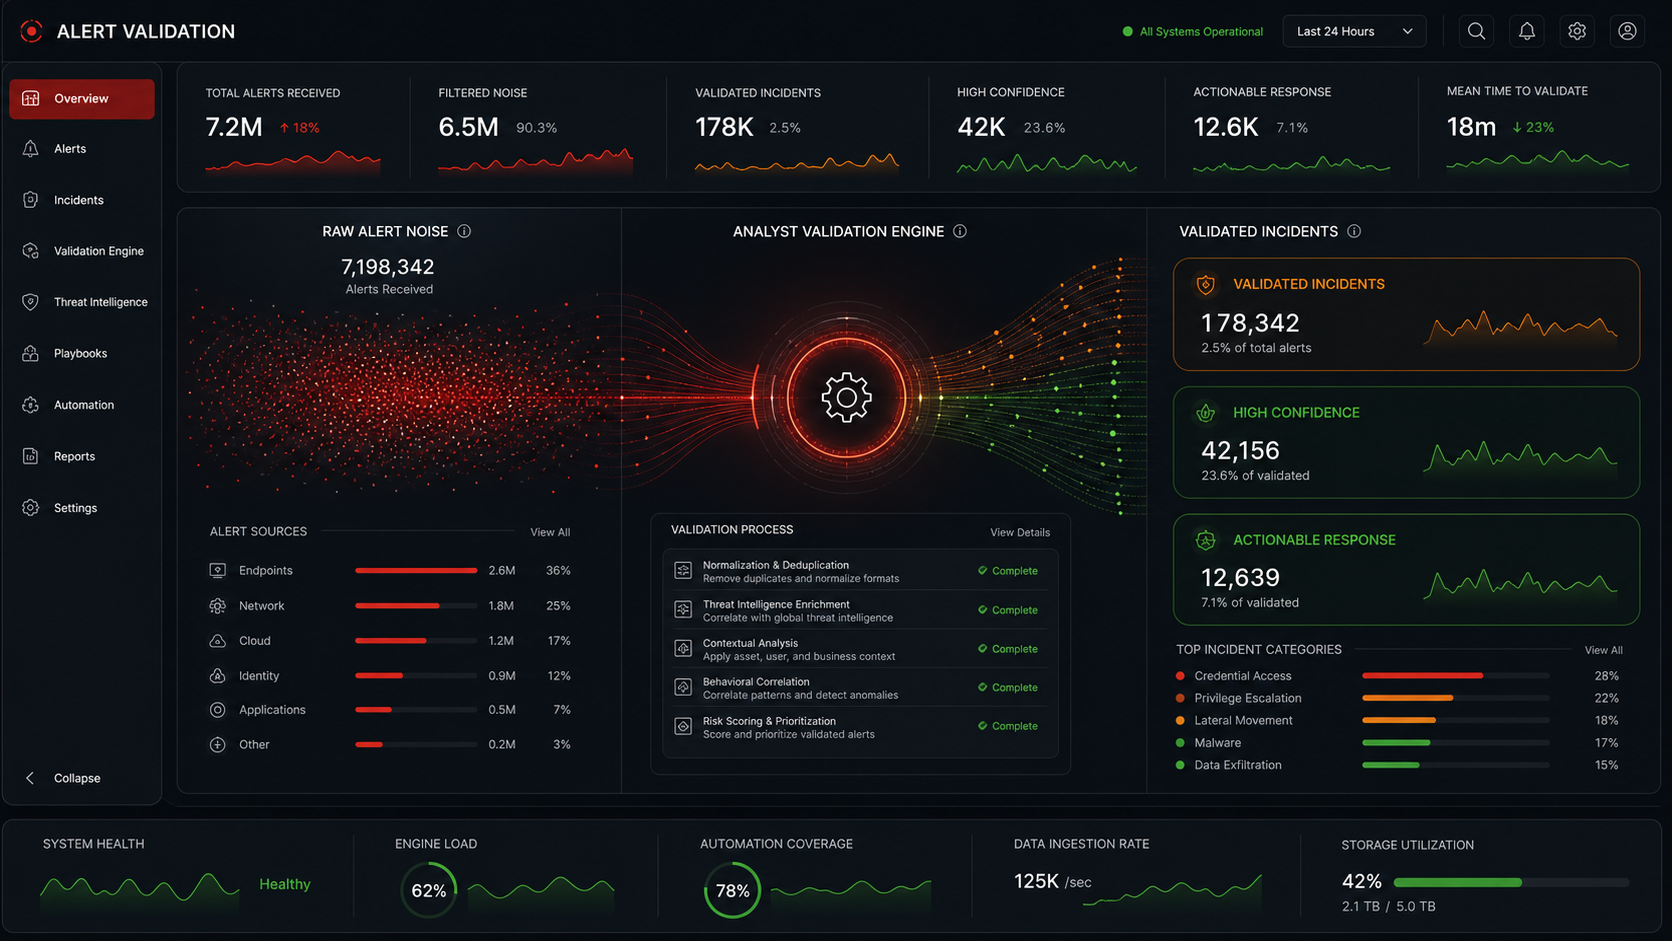
Improve Visibility Across Your Attack Surface.
CyberPhore connects telemetry from critical environments into one detection fabric, giving analysts the context needed to separate suspicious activity from business-as-usual behavior.
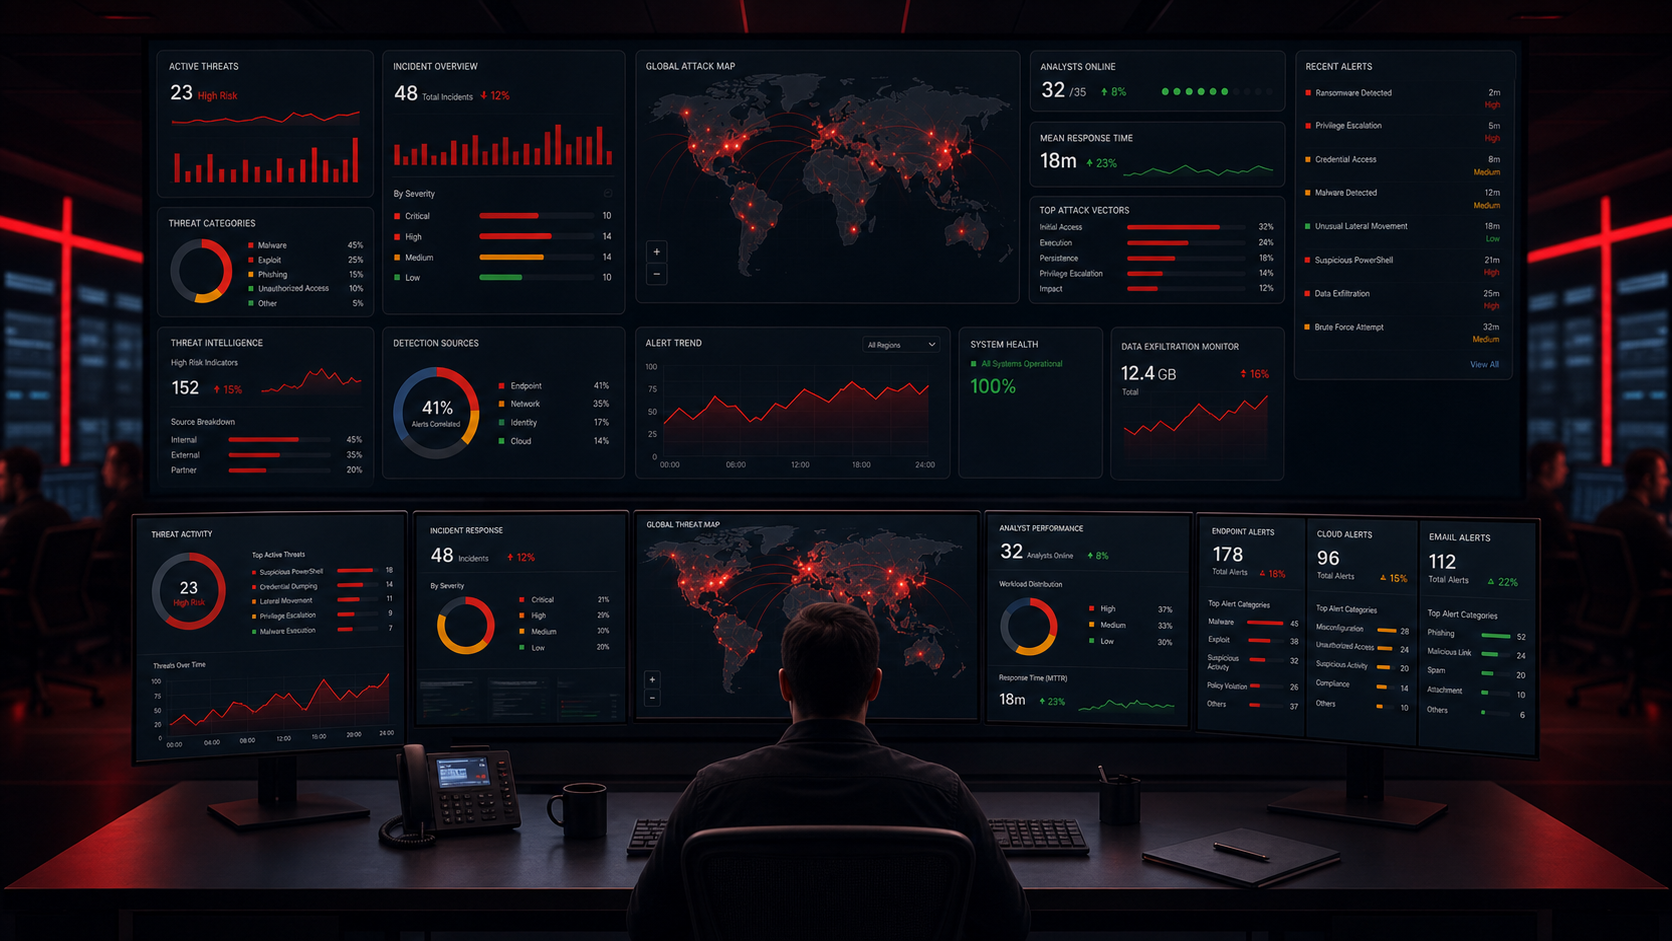
Investigation Workflow
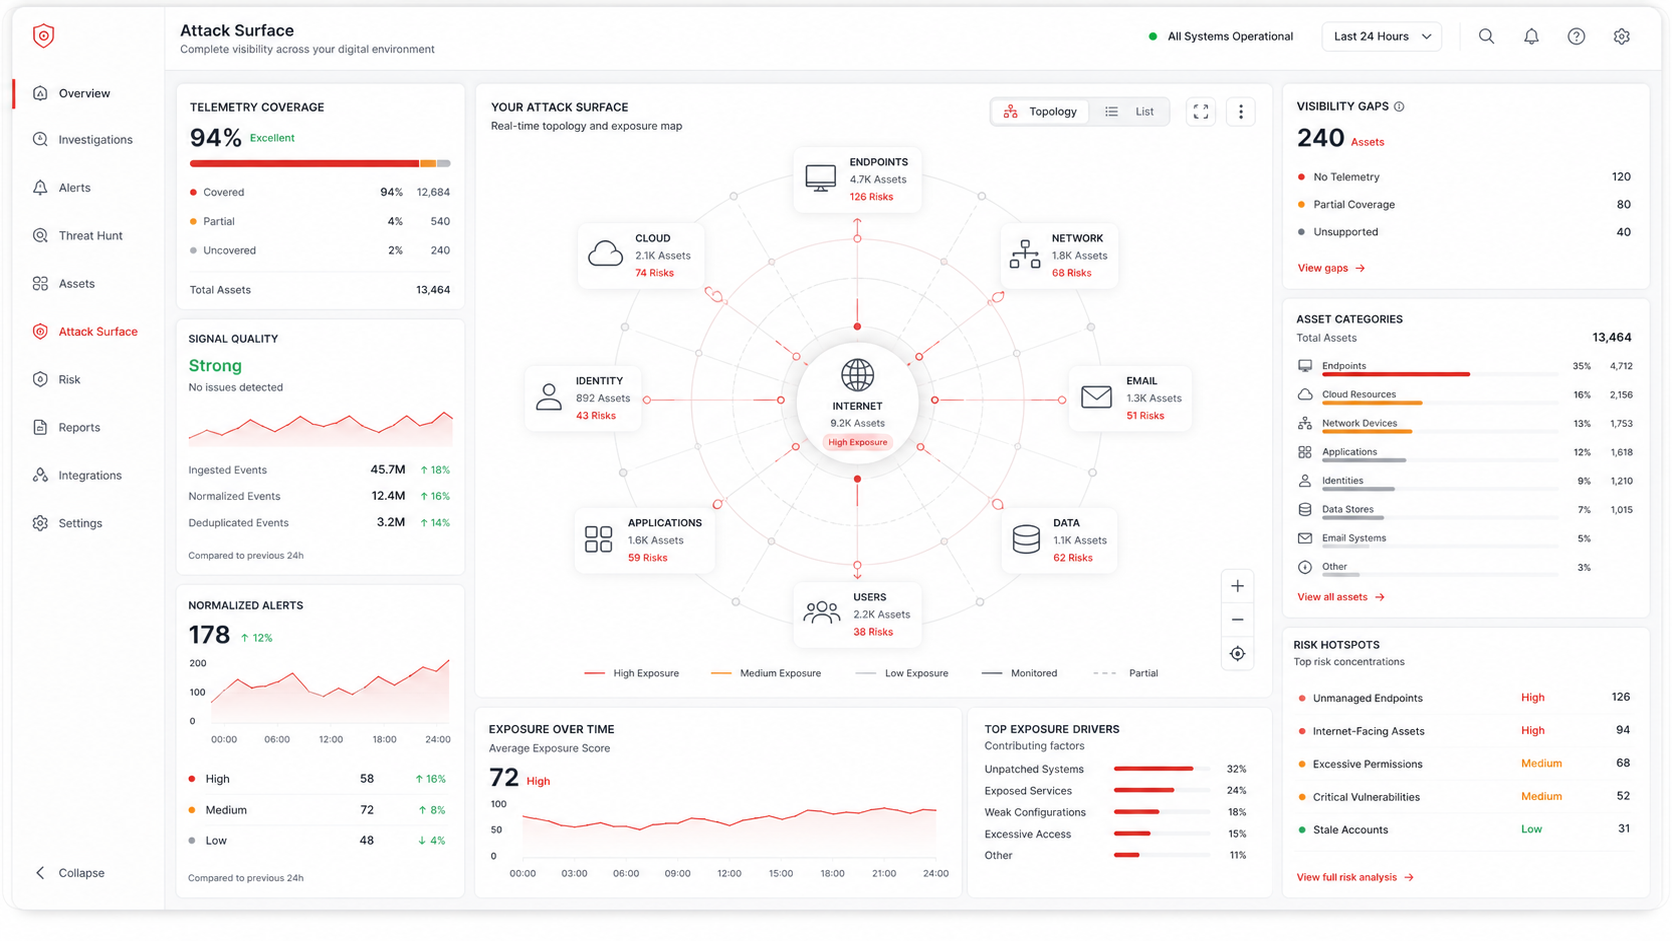
From Prioritized Signals To Response Guidance.
Prioritized signals can be reviewed with supporting context so your team receives clear investigation findings and practical response guidance.
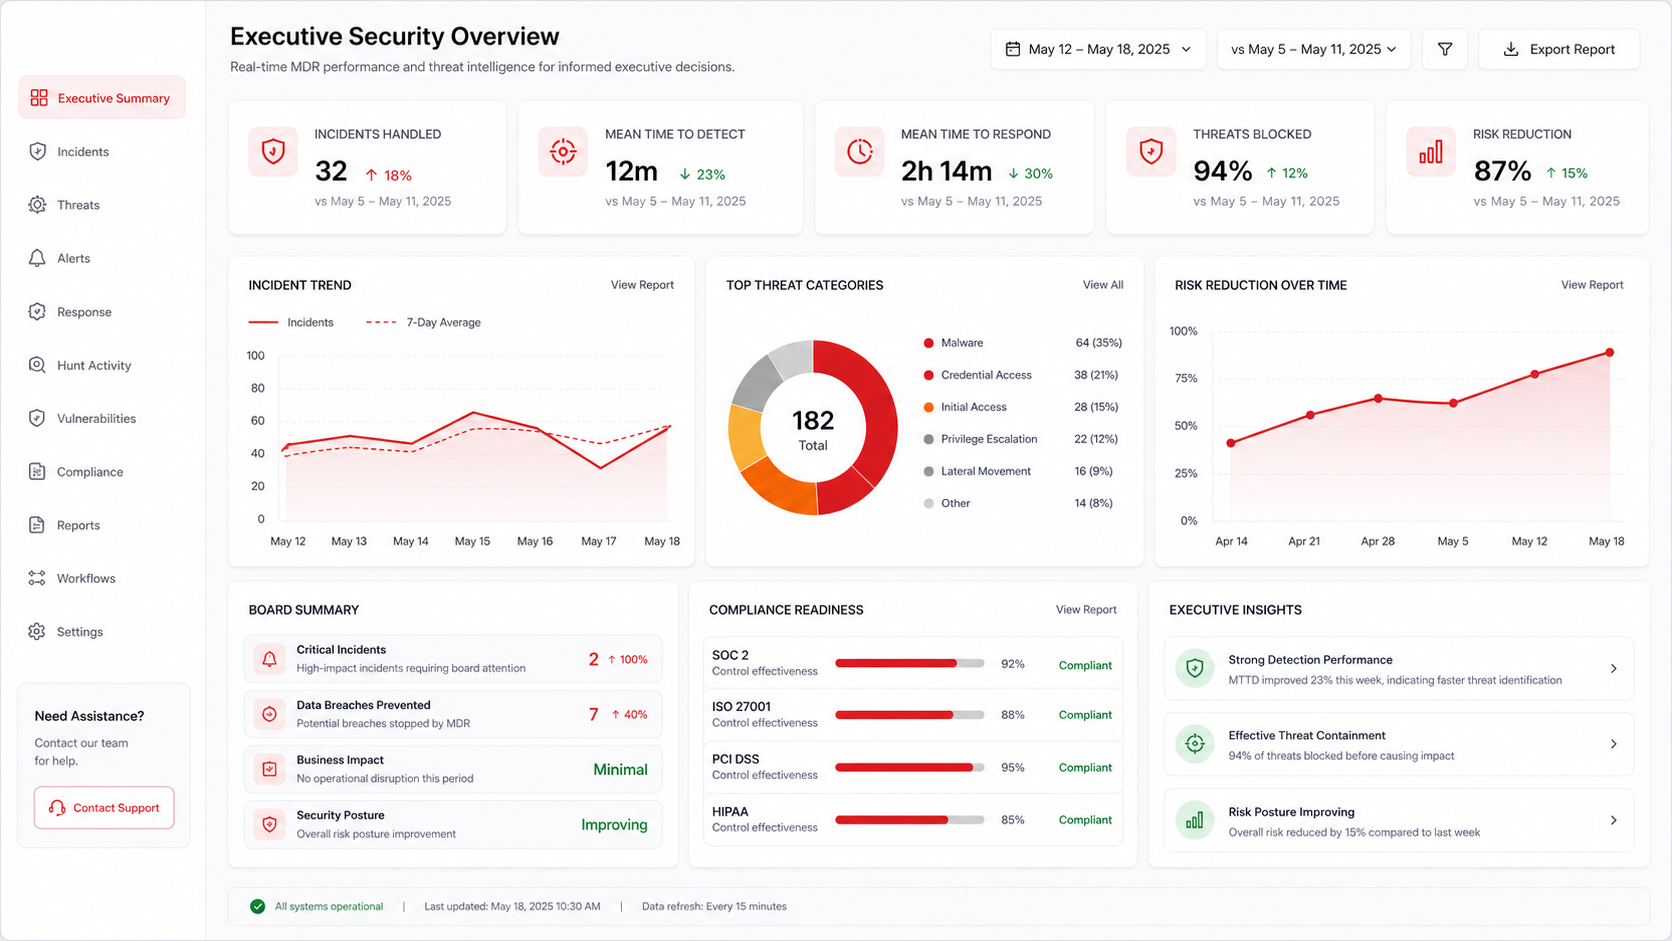
Executive Reporting
Security Insights That Drive Business Decisions.
Modern MDR reporting gives leaders the right metrics in the right context, connecting operational security work to risk, governance, and business confidence.
Connected Security
MDR Works Best As Part Of A Security Program.
Detection becomes stronger when endpoint, cloud, email, network, identity, vulnerability management, incident response, and compliance signals reinforce one another.
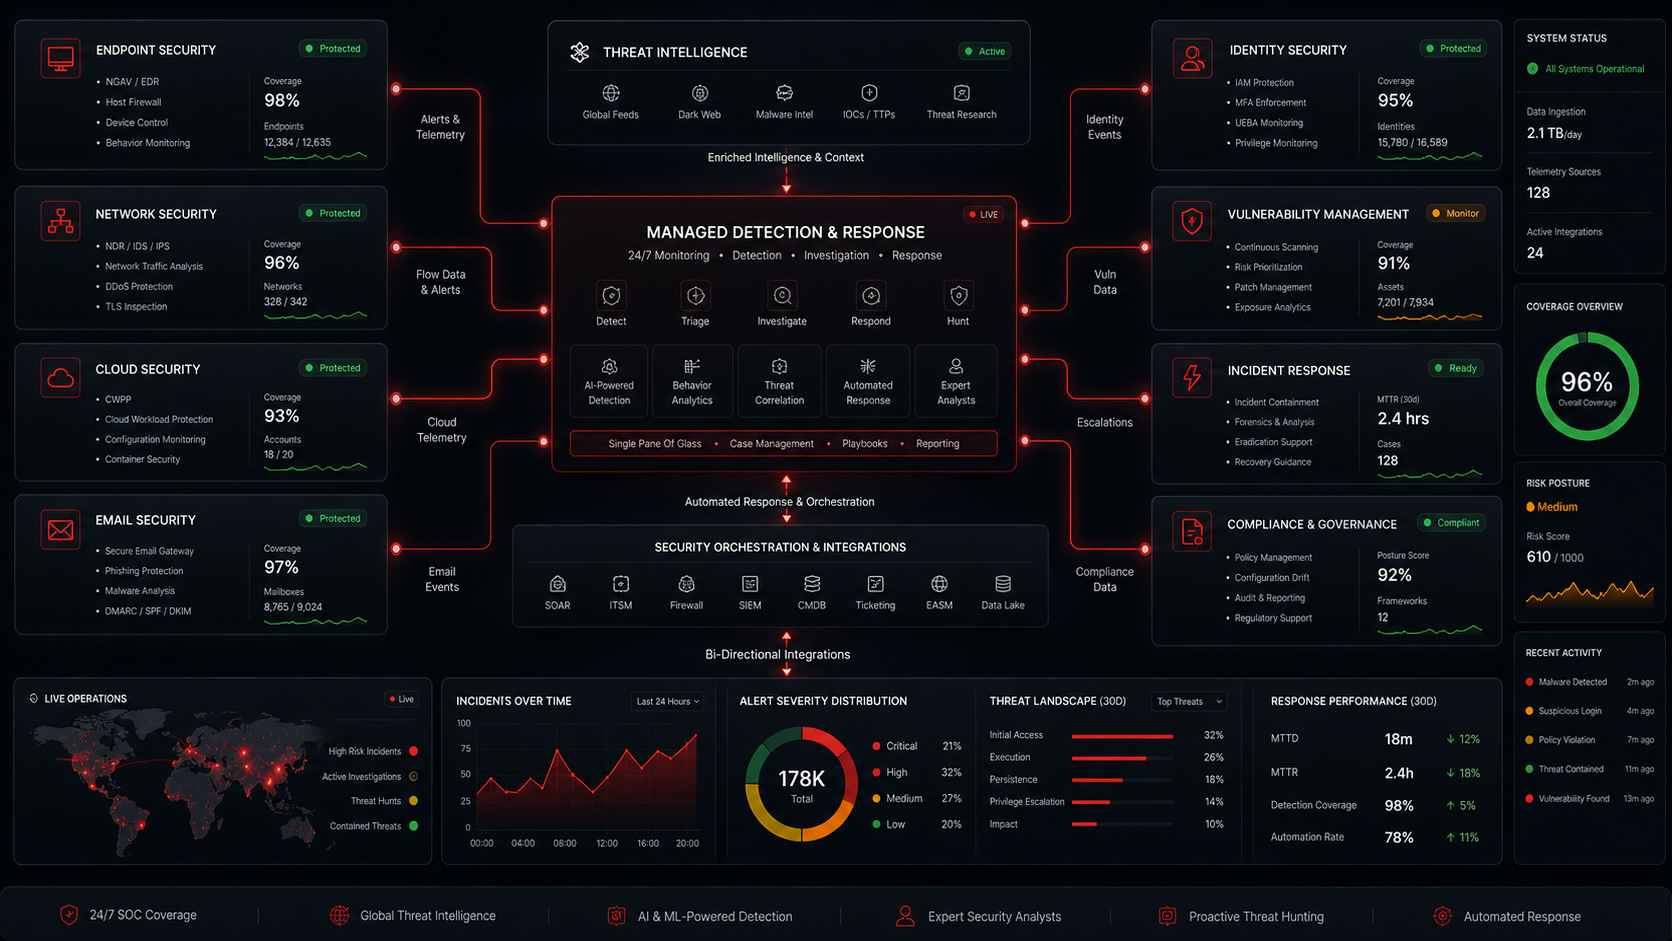
What MDR Includes
Built For Enterprise Security Operations.
A mature MDR service should improve signal quality, investigation depth, containment clarity, and leadership visibility.
MDR Buying Questions
Managed Detection And Response FAQs.
Clear answers for security leaders comparing MDR providers, SOC coverage, analyst investigation, and response support.
What Is Managed Detection And Response?
Managed detection and response combines continuous monitoring, analyst-led investigation, threat validation, threat hunting, and response guidance to help organizations detect and respond to active threats.
How Is MDR Different From Basic Security Monitoring?
Basic monitoring forwards alerts. MDR investigates signals, validates threat context, reduces false positives, prioritizes risk, and provides response-ready evidence and guidance.
How Is CyberPhore MDR Monitoring Scoped?
Monitoring hours, telemetry sources, escalation paths, investigation workflows, and response responsibilities are confirmed during consultation and documented for the agreed service scope.
Who Should Use Managed Detection And Response Services?
MDR is useful for organizations that need stronger detection, faster triage, threat hunting, security operations support, response guidance, and improved visibility across endpoint, identity, cloud, network, and email environments.
Ready To Strengthen Detection And Response?
Extend Your Team With Detection And Response Support.
Strengthen your security operations with monitoring, investigation, and response guidance aligned to your environment and agreed service scope.